Department of parliamentary services(DPS) have confirmed that personal mobile numbers of several federal politicians, their staff, and former prime ministers have mistakenly been published online.
The DPS, after every six months, publish the details of each politician and some former prime ministers on the spending of their mobile phones and internet which only includes their names and the amount of their bill with other information redacted.
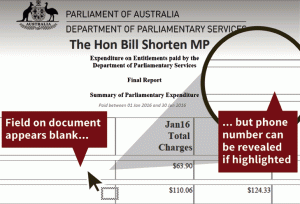
However, the latest information released in January 2016 contains the mobile phone numbers of several MPs, senators, and many ministers.
Some of the lucky officials were those whose numbers were not exposed in the report that includes, Prime Minister Malcolm Turnbull, Treasurer Scott Morrison, Attorney-General George Brandis and a few others.
Prime Minister Malcolm Turnbull and Environment and Energy Minister Josh Frydenberg at Parliament Housein Canberra. Photo: Alex Ellinghausen
Whereas, along with other staffers Opposition Leader Bill Shorten, Deputy Prime Minister Barnaby Joyce, Christopher Pyne, Mitch Fifield and Christian Porter have to compromise their contact numbers. Yet, the numbers of Former prime ministers Julia Gillard, John Howard and Paul Keating had also been exposed in the report.
The phone numbers were readable due to certain parts which were highlighted when opened on a computer.
The DPS had accused TELCO management, a private contractor, for the incident.
“In the most recent report provided by the contractor, it became possible to view the official mobile phone number of parliamentarians and their staff even though they appeared redacted from the published files,” A spokesperson said.
“The DPS removed the documents from the APH website shortly after it was alerted to the issue and is working with the contractor to investigate the cause.
“The DPS will work with parliamentarians to address privacy concerns and change mobile numbers if required.”
Greg Austin, a security expert believes that the breach could help foreign power in intelligence collection.
“I wouldn’t see it necessarily as leading directly to significant exposure,” said professor Austin, associated with Australian Centre for Cyber Security at UNSW.
“But this sort of data can form part of an intelligence picture for foreign intelligence agencies and can be used in a number of ways after that. Knowing the private phone numbers of these people also helps foreign intelligence agencies from a view of who is talking to who. So it’s not good.”
Whereas, the exposed contact details includes those of the members from minor parties including Greens leader Richard Di Natale.
Former Liberal ministers Andrew Robb and Jamie Briggs were also in the exposed contact list with other Retired MPs.
For more than three months, the contact information of all MPs who served between January and June last year, before the July election were accessible by general public very easily.
However, after reported by Fairfax Media, the details were deleted on Monday by DPS.
Also, the TELCO management has been contacted for comment.
Share this article
About the Author

Zehra Ali is a Tech Reporter and Journalist. She has done her Masters in Mass Communication. Topics related to cybersecurity, IoT, AI, Big Data and other privacy matters are extensively covered by her on various platforms. You can follow her on twitter.
More from Zehra AliRelated Posts

Google and FBI Disrupt NetNut Residential Proxy Network Used by 2M+ Devices
Google worked with the FBI and Lumen to disrupt the NetNut residential proxy network, also known as ...

Opera Launches Paste Protect to Block ClickFix Clipboard Attacks
Opera’s Paste Protect blocks harmful commands from reaching the clipboard, preventing ClickFix...

Reddit Introduces Mandatory Age Verification for EU Teens Accessing NSFW Content
Reddit will require European Union users under 18 to verify their age before viewing mature or NSFW ...

Popular ‘Adblock for YouTube’ Chrome Extension Found With Remote Code Execution Risk
The popular “Adblock for YouTube” Chrome extension now carries an architectural weakness...

Texas Hunting and Fishing License Data Breach Affects 3 Million Customers
Approximately 3 million Texas hunting and fishing license customers were affected by a data breach i...

FBI Warns of ‘Kali365’ Subscription Service Targeting Microsoft 365 Accounts
The FBI’s sounding the alarm on Kali365, a site where criminals can pick up ready-to-use tools for s...