How Donald Trump won US Presidential Election is still a mystery to some. People actually voted him for the president? Or did he hijacked election with the help of friends at Russia who hacked it?
In less than six hours, after the win of Donald Trump for the 2016 45th US Presidential Election, a surge of opportunist cyber attacks raised to target the US-policy think tanks via spear phishing campaign to lure them into installing malware with slogans like ‘The “shocking” truth about US election rigging,’ and similar.
The state-wide threat actors, also known with different monikers APT29, CozyDuke, Cozy Bear, and now ‘The Dukes’ was the culprit behind data breach of Democratic National Committee (DNC) and is alleged to have ties with the Russian government, according to the US bureaucrats. Russia, on the other end, rebuked such allegations and asked for answers. However, both the parties were unable to provide evidence.
On Wednesday, the hacking group launched its state-wide attack (post US presidential election) of spear phishing email on its victims including the US think tanks, NGOs, and US government insiders, pointed out by the experts at a security firm Volexity.
According to the experts, the attackers used compromised e-mail accounts at Harvard’s Faculty of Arts and Sciences (FAS), and the launched the attack in 5 different waves. The targets were individuals and organizations focusing on international affairs, national security, defense, public policy, and the European and Asian studies.
Two of the attacks pretended to come from Clinton Foundation giving insights on elections. Two attacks purported to be eFax links or documents about elections being rigged or revised, and the last attack shipped with a PDF file link related to ‘Why American Elections Are Flawed.’ The firm believes that these attacks are carried out by ‘The Dukes.’
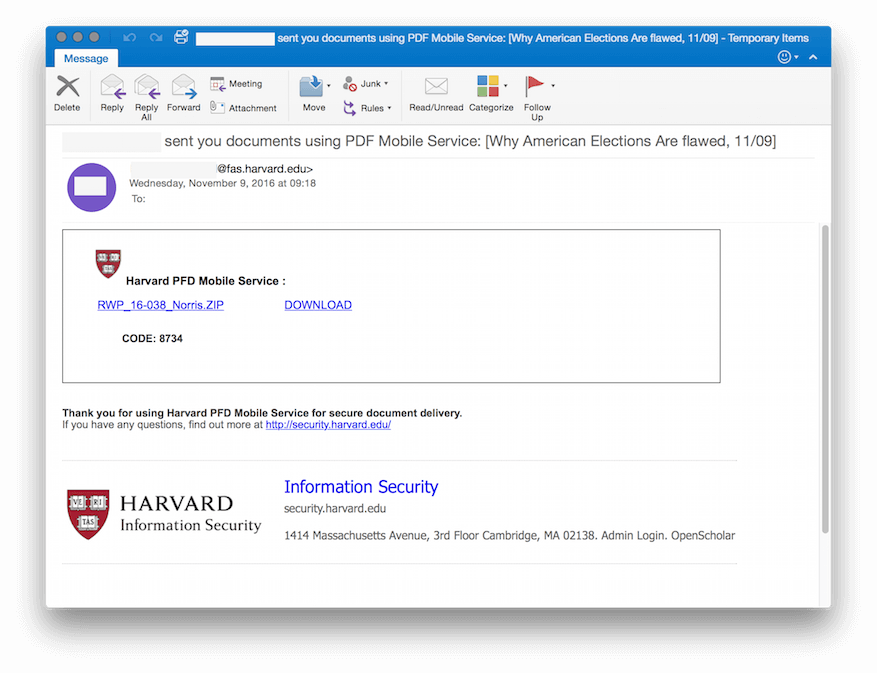
According to experts, the e-mails pretended to come from Harvard’s ‘PDF Mobile Service’ or ‘PFD Mobile Service’ that is non-existent service in Harvard. The typographical error was inconsistent in the e-mails but was consistent with the domain name registered by the attackers.
Volexity reports, “[The malware] had tremendous success evading anti-virus and anti-malware solutions at both the desktop and mail gateway levels. The group’s anti-VM macros and PowerShell scripts appear to have drastically reduced the number of sandboxes and bots that the group has to deal with on their command and control infrastructure.”
Photo Credit: Volexity
Share this article
About the Author

Peter Buttler an Infosec Journalist and Tech Reporter, Member of IDG Network. In 2011, he completed Masters in Cybersecurity and technology. He worked for leading security and tech giants as Staff Writer. Currently, he contributes to a number of online publications, including The Next Web, CSO Online, Infosecurity Mag, SC Magazine, Tripwire, GlobalSign CSO Australia, etc. His favorite areas Online Privacy, AI, IoT, VR, Blockchain, Big Data, ML, Fintech, etc. You can follow him on twitter.
More from Peter ButtlerRelated Posts

Google and FBI Disrupt NetNut Residential Proxy Network Used by 2M+ Devices
Google worked with the FBI and Lumen to disrupt the NetNut residential proxy network, also known as ...

Opera Launches Paste Protect to Block ClickFix Clipboard Attacks
Opera’s Paste Protect blocks harmful commands from reaching the clipboard, preventing ClickFix...

Reddit Introduces Mandatory Age Verification for EU Teens Accessing NSFW Content
Reddit will require European Union users under 18 to verify their age before viewing mature or NSFW ...

Popular ‘Adblock for YouTube’ Chrome Extension Found With Remote Code Execution Risk
The popular “Adblock for YouTube” Chrome extension now carries an architectural weakness...

Texas Hunting and Fishing License Data Breach Affects 3 Million Customers
Approximately 3 million Texas hunting and fishing license customers were affected by a data breach i...

FBI Warns of ‘Kali365’ Subscription Service Targeting Microsoft 365 Accounts
The FBI’s sounding the alarm on Kali365, a site where criminals can pick up ready-to-use tools for s...