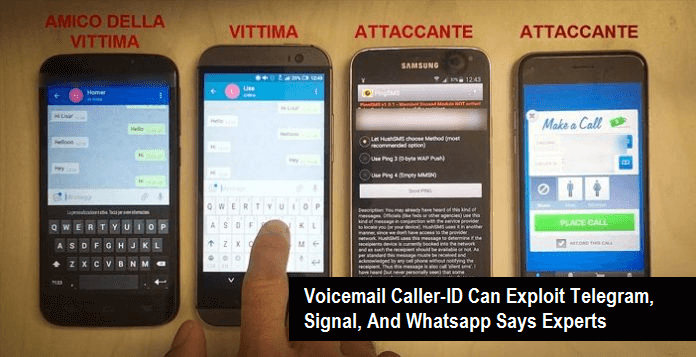
Italian cyber security experts have found a voicemail caller-ID vulnerability that can potentially be exploited to hack into the messaging apps such as Telegram, Signal, and Whatsapp.
According to InTheCyber experts, an old voicemail caller-ID spoof can be leveraged into stealing activation codes sent from messaging apps services and compromise the victim’s account. The experts said that the there are two major network operators in Italy, that allows such kind of attack, and an attacker only requires victim’s phone number to carry a successful attack.
Based in Lugano and Milan, the security firm InTheCyber explained in a blog post that the bug can be exploited in three different scenarios and all those scenarios require victim not to respond, engaged in a conversation, and not reachable.
The concept behind this attack is that messaging apps like Signal, Telegram, and Whatsapp send an activation code via SMS when requested. If the SMS fails or doesn’t comply promptly, it then sends the activation code via an automated call. Thus, if the user does not respond, the call leaves a voicemail for the user to respond it later. The attacker simply needs to spoof the caller-ID in order to retrieve the activation code.
Since calls are sent to voicemail when a user is occupied, does not respond, or is unreachable, the attacker can execute the attack to leverage all three possible scenarios. An attacker can send silent-SMS to determine whether the phone is unreachable and detach from the network. He can request the activation code late at night and could set up a scam to keep the phone in a busy state during the attack.
Once the code is sent to the voicemail, the attacker can spoof the caller-ID to impersonate as the victim and retrieve both the voicemail and activation code. The experts have demonstrated the attack in a video for the explanation and publicized the details on Monday, at ‘Cyber Warfare’ 7th National Conference in Milan.
The researcher estimates that roughly 32 million users are at risk who are using H3G and Wind. The immediate solution is to turn off the voicemail, while both the wireless carriers and messaging app service providers look into the matter and resolve it.
Share this article
About the Author

Peter Buttler an Infosec Journalist and Tech Reporter, Member of IDG Network. In 2011, he completed Masters in Cybersecurity and technology. He worked for leading security and tech giants as Staff Writer. Currently, he contributes to a number of online publications, including The Next Web, CSO Online, Infosecurity Mag, SC Magazine, Tripwire, GlobalSign CSO Australia, etc. His favorite areas Online Privacy, AI, IoT, VR, Blockchain, Big Data, ML, Fintech, etc. You can follow him on twitter.
More from Peter ButtlerRelated Posts

Google and FBI Disrupt NetNut Residential Proxy Network Used by 2M+ Devices
Google worked with the FBI and Lumen to disrupt the NetNut residential proxy network, also known as ...

Opera Launches Paste Protect to Block ClickFix Clipboard Attacks
Opera’s Paste Protect blocks harmful commands from reaching the clipboard, preventing ClickFix...

Reddit Introduces Mandatory Age Verification for EU Teens Accessing NSFW Content
Reddit will require European Union users under 18 to verify their age before viewing mature or NSFW ...

Popular ‘Adblock for YouTube’ Chrome Extension Found With Remote Code Execution Risk
The popular “Adblock for YouTube” Chrome extension now carries an architectural weakness...

Texas Hunting and Fishing License Data Breach Affects 3 Million Customers
Approximately 3 million Texas hunting and fishing license customers were affected by a data breach i...

FBI Warns of ‘Kali365’ Subscription Service Targeting Microsoft 365 Accounts
The FBI’s sounding the alarm on Kali365, a site where criminals can pick up ready-to-use tools for s...