America is apprehensive about whether $50 smartphones from China surveillance over it through backdoor software or was a supply chain mistake.
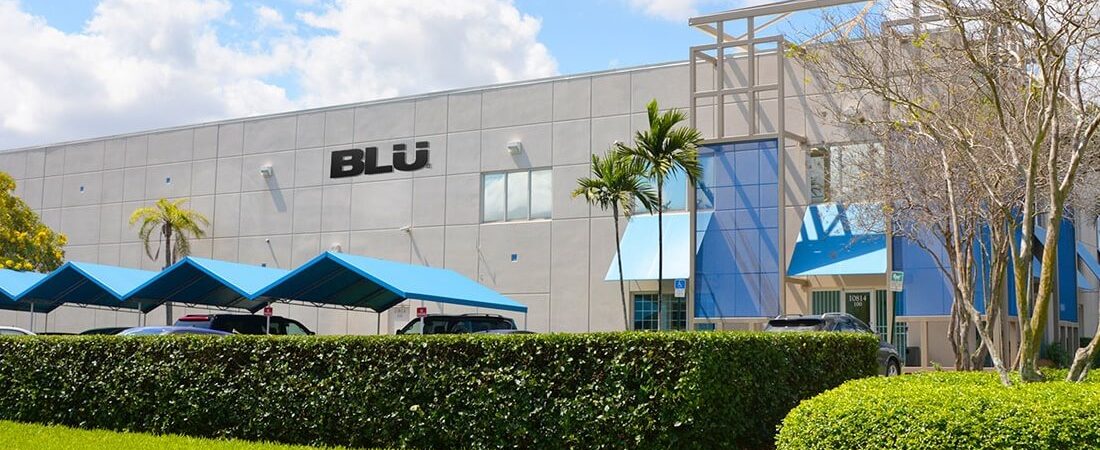
Security experts at Kryptowire firm have identified a backdoor software pre-installed on low-budget and disposable Chinese variants of mobile phones. The backdoor was found pre-installed in the mobile phones distributed by the company named BLU.
The backdoor software resides in the FOTA – Firmware Over The Air – that allows businesses to update their firmware remotely. The company AdUps provides updated software to BLU Android devices.
The USA-based phone manufacturer BLU products told NYTimes that 120,000 of its phones were affected and they have updated the software to remove the feature.
Kryptowire said the Adups software transmitted the full contents of contact lists, text messages, call logs, location information and other data to a Chinese server. These servers appear to be owned by Shanghai AdUps Technologies.
“Kryptowire has identified several models of Android mobile devices that contained firmware that collected sensitive personal data about their users and transmitted this sensitive data to third-party servers without disclosure or the users’ consent. These devices were available through major US-based online retailers (Amazon, BestBuy, for example) and included modern smartphones such as the BLU R1 HD.” Kryptowire published analysis reads, “These devices actively transmitted user and device information including the full-body of text messages, contact lists, call history with full telephone numbers, unique device identifiers including the International Mobile Subscriber Identity (IMSI) and the International Mobile Equipment Identity (IMEI).“
Adups seems to defend its stance by saying that “This is a private company that made a mistake,” spoken via its lawyer Lily Lim.
According to Adups, the software was written for an unidentified Chinese manufacturer who wanted to use the data for customer support. The software was intended to help the client identify junk calls and text messages. Moreover, she doesn’t know how many phones were affected.
She further said that the company, not Adups, is responsible for disclosing privacy policies to its customers. Adups only provide the functionality that its distributors ask for.
Adups provides firmware updates for major mobile manufacturers, including ZTE and Huawei, and its code runs on more than 700 million mobiles, cars, and other smart devices.
However, the Adups lawyer told the NYT that the company is not involved in any government surveillance program and assured that the data collection for the BLU product has already been destroyed.
NYT reported, “For many years, the Chinese government has used a variety of methods to filter and track Internet use and monitor online conversations. It requires technology companies that operate in China to follow strict rules. Ms. Lim said Adups was not affiliated with the Chinese government.”
Kryptowire reported its findings to the US government and made its report public on Tuesday.
A spokeswoman for the Department of Homeland Security, Marsha Catron, said, “was recently made aware of the concerns discovered by Kryptowire and is working with our public and private sector partners to identify appropriate mitigation strategies.”
Share this article
About the Author

Peter Buttler an Infosec Journalist and Tech Reporter, Member of IDG Network. In 2011, he completed Masters in Cybersecurity and technology. He worked for leading security and tech giants as Staff Writer. Currently, he contributes to a number of online publications, including The Next Web, CSO Online, Infosecurity Mag, SC Magazine, Tripwire, GlobalSign CSO Australia, etc. His favorite areas Online Privacy, AI, IoT, VR, Blockchain, Big Data, ML, Fintech, etc. You can follow him on twitter.
More from Peter ButtlerRelated Posts

Google and FBI Disrupt NetNut Residential Proxy Network Used by 2M+ Devices
Google worked with the FBI and Lumen to disrupt the NetNut residential proxy network, also known as ...

Opera Launches Paste Protect to Block ClickFix Clipboard Attacks
Opera’s Paste Protect blocks harmful commands from reaching the clipboard, preventing ClickFix...

Reddit Introduces Mandatory Age Verification for EU Teens Accessing NSFW Content
Reddit will require European Union users under 18 to verify their age before viewing mature or NSFW ...

Popular ‘Adblock for YouTube’ Chrome Extension Found With Remote Code Execution Risk
The popular “Adblock for YouTube” Chrome extension now carries an architectural weakness...

Texas Hunting and Fishing License Data Breach Affects 3 Million Customers
Approximately 3 million Texas hunting and fishing license customers were affected by a data breach i...

FBI Warns of ‘Kali365’ Subscription Service Targeting Microsoft 365 Accounts
The FBI’s sounding the alarm on Kali365, a site where criminals can pick up ready-to-use tools for s...