Neglecting to password-protect a database backup, an American organization has exposed about 1.37 billion personal account details and email addresses online, ended up in data leaking online which could be seen by anyone poking around. Even the details weren’t secured by username or password.
A data breach hunter with MacKeeper, Chris Vickery, pointed out the issue along with CSOOnline and Spamhaus, the anti-spam group and released the details of the finding.
An outfit River City Media (RCM), run by spammers Alvin Slocombe and Matt Ferris, has leaked the files, Vickery wrote in his findings.
Vickery said the outfit was sending as many as a billion emails every day. However, the outfit claimed it as a legitimate marketing operation.
Some of the documents show how cost-effective spamming could be. A single day of activity that targeted Gmail users with 18 million emails and AOL users with another 15 million is shown by one leaked text. The total take: is around $36,000.
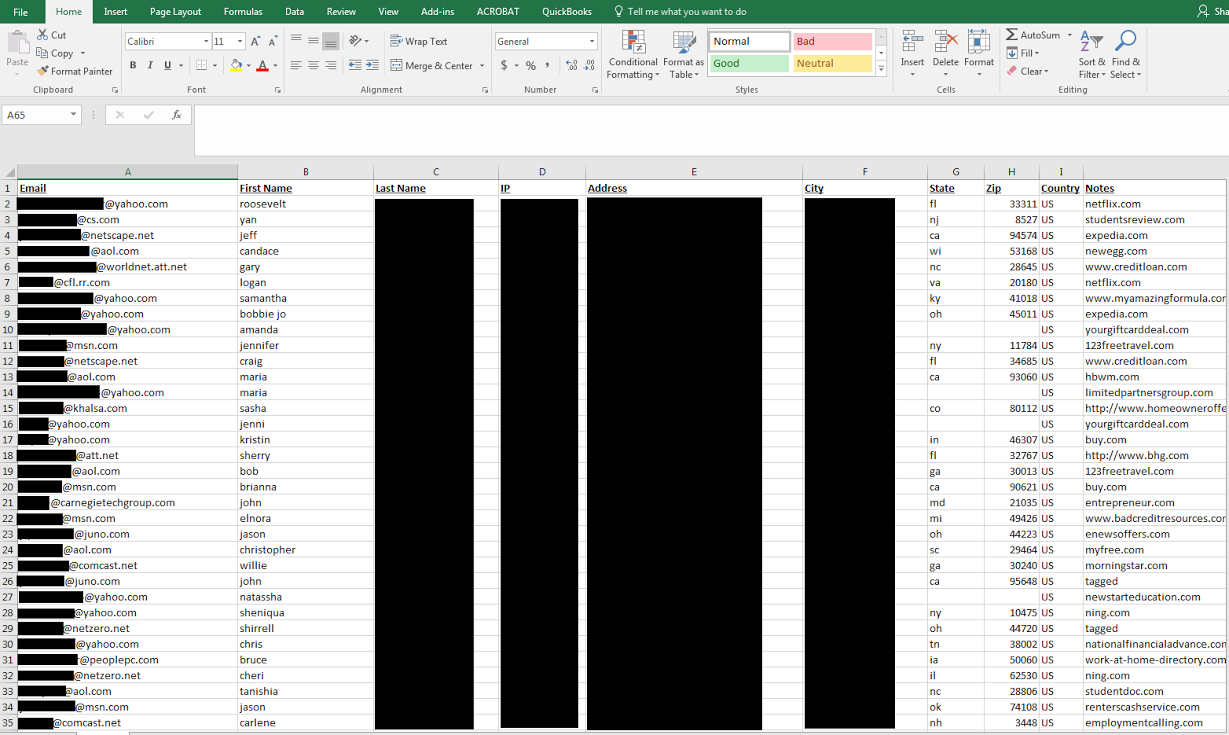
According to Vickery, through research over many years, automation and illegal hacking practices, the goal was achieved.
Microsoft, Apple, and other franchises had been informed of the details of the script and technique. Also, the law enforcement authorities are appraised, Vickery wrote.
https://twitter.com/VickerySec/status/838817731038191616?ref_src=twsrc%5Etfw
To ensure that the details are not faked, he looked up the names of certain people in the leaked list so as to authenticate them further.
There were several military email accounts whose IP addresses and full names were also present.
Chris Vickery wrote in detail that it is the initial reaction and natural response to asking about the dataset is it real or not.
“I’m still struggling with the best software solution to handle such a voluminous collection, but I have looked up several people that I know and the entries are accurate,” he further added.
According to him, the only thing saving grace is that some are outdated in these few years and the subject no longer lives in the same location.
The entire structure used by RCM is blacklisted by Spamhaus.
Share this article
About the Author

Zehra Ali is a Tech Reporter and Journalist. She has done her Masters in Mass Communication. Topics related to cybersecurity, IoT, AI, Big Data and other privacy matters are extensively covered by her on various platforms. You can follow her on twitter.
More from Zehra AliRelated Posts

Google and FBI Disrupt NetNut Residential Proxy Network Used by 2M+ Devices
Google worked with the FBI and Lumen to disrupt the NetNut residential proxy network, also known as ...

Opera Launches Paste Protect to Block ClickFix Clipboard Attacks
Opera’s Paste Protect blocks harmful commands from reaching the clipboard, preventing ClickFix...

Reddit Introduces Mandatory Age Verification for EU Teens Accessing NSFW Content
Reddit will require European Union users under 18 to verify their age before viewing mature or NSFW ...

Popular ‘Adblock for YouTube’ Chrome Extension Found With Remote Code Execution Risk
The popular “Adblock for YouTube” Chrome extension now carries an architectural weakness...

Texas Hunting and Fishing License Data Breach Affects 3 Million Customers
Approximately 3 million Texas hunting and fishing license customers were affected by a data breach i...

FBI Warns of ‘Kali365’ Subscription Service Targeting Microsoft 365 Accounts
The FBI’s sounding the alarm on Kali365, a site where criminals can pick up ready-to-use tools for s...